One platform · All native · AI enabled · Backed by a highly responsive service
We watch, protect and manage your security. Continuously.
ThiRU monitors every asset you own, stops threats as they happen and manages your security risk end to end, as one complete service. It runs on our own platform, engineered by ThiRU from the agent to the AI to the console. It is not a dashboard stitched over other vendors' tools.
- One platformEvery capability in one place
- All nativeBuilt by ThiRU, no third-party stitching
- AI enabledDetects and contains in real time
- Responsive serviceAnalysts on call 24/7, minutes to respond
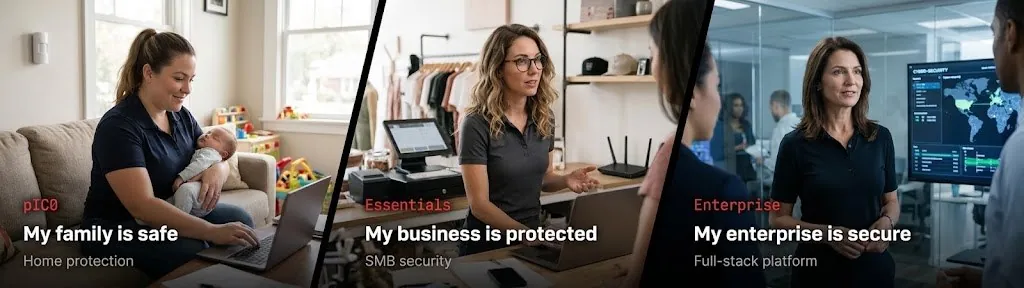
Who we protect
One platform for your home, your business and your enterprise
99.9%Uptime guarantee
<10msThreat detection
24/7Monitoring and support
500+Enterprise clients
Built, not bolted together
One platform, all native. Not a front end over someone else's tools.
Many security services put a dashboard on top of five or six vendors' products and resell the bundle. Every handoff between those products is a place where alerts get lost, data gets out of step and nobody owns the outcome. ThiRU owns the whole stack, so one team is accountable for your protection.
Typical multi-vendor service
A dashboard over a patchwork
Reseller dashboard
- EDR vendor
- SIEM vendor
- Email vendor
- Firewall vendor
- Intel feed
- Ticketing
⚠ separate agents, licences, data formats and support desks
- Alerts translated between products, with delays and blind spots in the gaps
- Several agents slowing every device
- When something breaks, each vendor points at another
- Your data spread across overseas clouds you don't control
The ThiRU platform
One platform, engineered end to end
- Console and reporting
- Response playbooks
- AI detection models
- Data pipeline and intel
- Agent on every device
- One agent, one data model, nothing lost between layers
- Detection to containment in minutes, not tickets between vendors
- One team accountable for your outcome
- Sovereign hosting in Australia or on ThiRU AI Data Centre nodes
- MonitorEvery asset, all the timeDevices, users, cloud, email and OT watched 24/7.
- ProtectStop threats as they landAI blocks and contains automatically.
- RespondAnalysts take overThiRU investigates, remediates and reports.
- Manage riskLower your exposureGaps, compliance and priorities reviewed with you.
↺ and back to monitoring, continuously
Threat intelligence
The latest advisories our analysts are acting on
- EXPLOITEDCVE-2026-118527: Ivanti Connect Secure Generation of Predictable Numbers or Identifiers VulnerabilityCISA known exploited · Ivanti Connect Secure · US federal patch deadline 2026-11-13
- EXPLOITEDCVE-2026-111357: Ivanti Connect Secure Missing Authentication for Critical Function VulnerabilityCISA known exploited · Ivanti Connect Secure · US federal patch deadline 2026-11-02
- EXPLOITEDCVE-2026-97229: GitLab Community Edition and Enterprise Edition Integer Overflow or Wraparound VulnerabilityCISA known exploited · GitLab Community Edition and Enterprise Edition · US federal patch deadline 2026-11-01
- EXPLOITEDCVE-2026-76418: Cisco Secure Firewall ASA Software and Cisco Secure FTD Software Unchecked Return Value to NULL Pointer Dereference VulnerabilityCISA known exploited · Cisco Secure Firewall ASA Software and Cisco Secure FTD Software · US federal patch deadline 2026-11-01
- EXPLOITEDCVE-2026-41709: Broadcom VMWare ESX Insufficient Logging VulnerabilityCISA known exploited · Broadcom VMware ESX · US federal patch deadline 2026-11-11
- EXPLOITEDCVE-2026-46300: Linux Kernel Missing Initialization of a Variable VulnerabilityCISA known exploited · Linux Kernel · US federal patch deadline 2026-10-31
ThiRU AI Security Operations Centre
Your AI-powered SOC, run by us on our own platform
ThiRU's AI SOC thinks, learns and acts across your whole attack surface. Our AI and our analysts work on the same data, in the same platform, so nothing is lost passing between vendors.
Autonomous threat detection
Models trained on millions of threat patterns watch your environment continuously and flag anomalies and zero-days in real time, without alert fatigue.
Automated incident response
AI playbooks contain a confirmed threat the moment it is detected, cutting mean time to respond from hours to minutes.
Continuous learning
The engine updates its detection models as your threat landscape shifts and correlates global intelligence to stay ahead of adversaries.
From sign-up to full protection in days
How onboarding works
Every step is handled by ThiRU. You keep your existing infrastructure, on-premises, cloud or hybrid.
- Step 01Sign up and scopeWe map your key assets and risk profile in a short scoping call.Day 0
- Step 02ConnectLightweight agents and cloud connectors deploy with zero downtime.Day 1–2
- Step 03AI baseliningThe AI engine learns what normal looks like, so real threats stand out from noise.Day 3–7
- Step 04Managed coverageSOC analysts monitor, respond and report around the clock from then on.Ongoing
ThiRU AI Data Centre
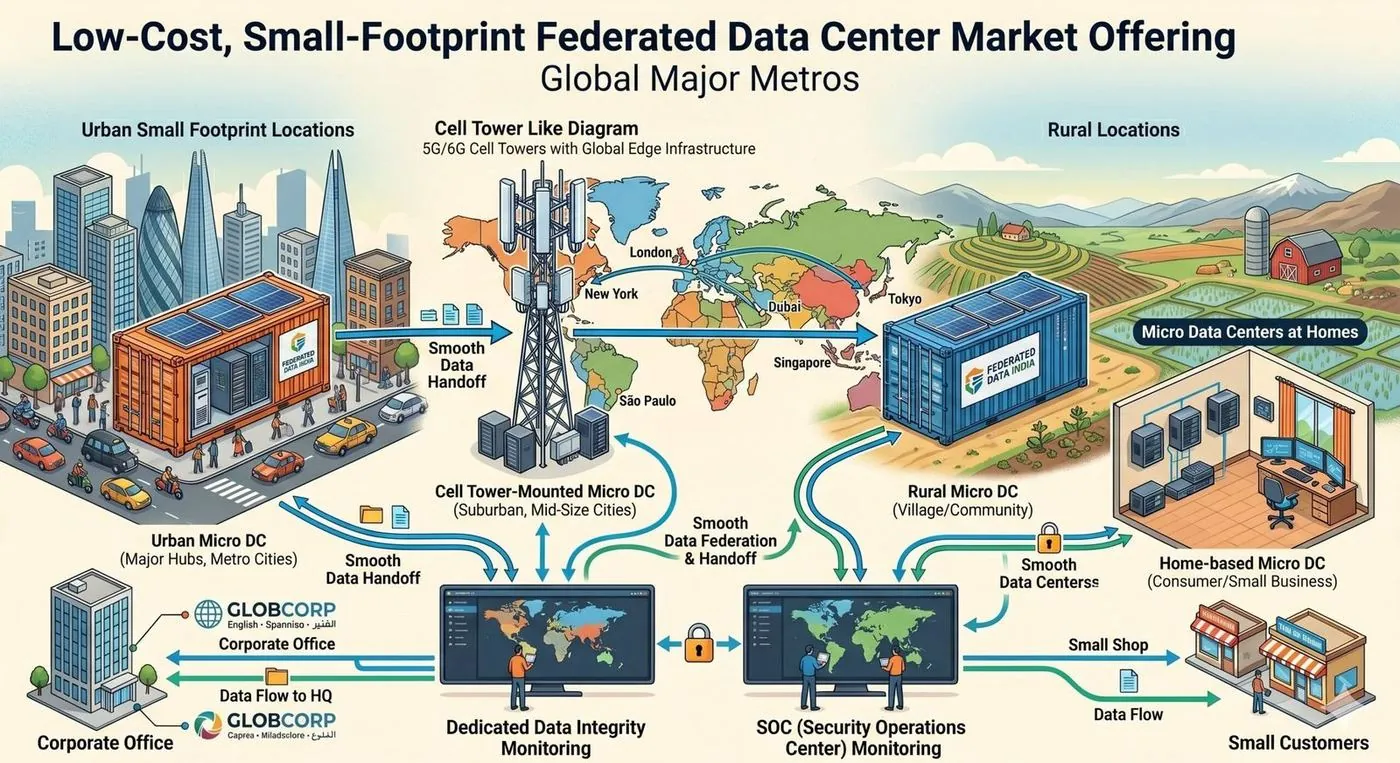
Sovereign compute, federated from the city to the village
Low-cost, small-footprint micro data centres, from a half-fridge cabinet at home to a 2 MW solar-powered site, federated into one network and watched by the same ThiRU SOC.
Built for the sectors that keep nations running
- Government
- Critical infrastructure
- Financial services
- Healthcare
- Defence
- Education
- Energy and utilities
- SME
In today's threat landscape, you don't have the luxury of reacting after an attack. ThiRU gives you the intelligence and response capability to act before the breach happens.
Dr. Suresh Hungenahally, Founder & CEO, ThiRU Labs
Get started
Ready to secure your digital future?
Talk to a ThiRU security specialist. Whether you need a managed SOC, a platform deployment or an OSINT assessment, we'll scope it with you.