Platform
Our platform, end to end
ThiRU builds and owns every layer: the agent on your devices, the data pipeline, the AI detection models, the response playbooks and the console. One agent per device, one data model, one team accountable for all of it.
ThiRU + Microsoft 365
Your business tools and your security, in one ecosystem
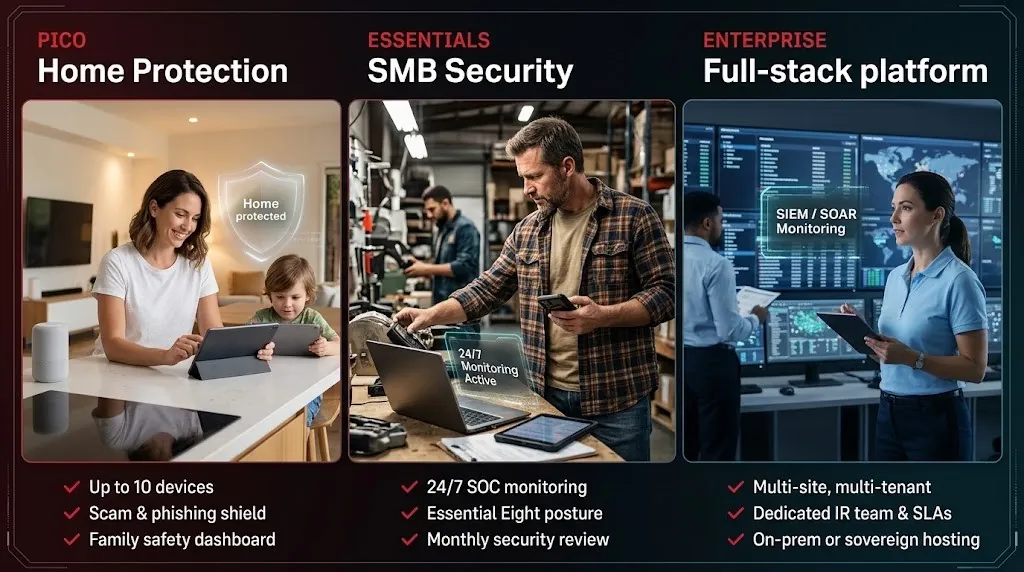
Run Microsoft 365 Business Basics and Office 365 for email, Teams, SharePoint and OneDrive. ThiRU's AI-enabled SOC monitors them alongside your VPN, browsers, SaaS apps, network traffic and cloud, then protects, mitigates and reports in one continuous loop.
Capabilities
What's inside every tenant
Unified dashboard
Event correlation across network, endpoint and cloud, with continuous asset inventory.
Automated playbooks
Host isolation, segmentation and forensic capture triggered on confirmation.
Compliance mapping
ISO 27001, NIST CSF, Essential Eight and PCI DSS evidence, collected continuously.
Threat intelligence
STIX/TAXII feeds, UEBA and MITRE ATT&CK-aligned predictive risk scoring.
OSINT engine
Attack-surface discovery, typosquat detection and leaked-credential alerts.
Dark web monitoring
Forums, marketplaces and paste sites watched for your data and brand.
Integrations
Slack, email, SMS, Jira, ServiceNow and PagerDuty out of the box.
Open API
REST API and webhooks for MSPs and in-house teams building on ThiRU.
Built, not bolted together
One platform, all native. Not a front end over someone else's tools.
Many security services put a dashboard on top of five or six vendors' products and resell the bundle. Every handoff between those products is a place where alerts get lost, data gets out of step and nobody owns the outcome. ThiRU owns the whole stack, so one team is accountable for your protection.
Typical multi-vendor service
A dashboard over a patchwork
Reseller dashboard
- EDR vendor
- SIEM vendor
- Email vendor
- Firewall vendor
- Intel feed
- Ticketing
⚠ separate agents, licences, data formats and support desks
- Alerts translated between products, with delays and blind spots in the gaps
- Several agents slowing every device
- When something breaks, each vendor points at another
- Your data spread across overseas clouds you don't control
The ThiRU platform
One platform, engineered end to end
- Console and reporting
- Response playbooks
- AI detection models
- Data pipeline and intel
- Agent on every device
- One agent, one data model, nothing lost between layers
- Detection to containment in minutes, not tickets between vendors
- One team accountable for your outcome
- Sovereign hosting in Australia or on ThiRU AI Data Centre nodes
- MonitorEvery asset, all the timeDevices, users, cloud, email and OT watched 24/7.
- ProtectStop threats as they landAI blocks and contains automatically.
- RespondAnalysts take overThiRU investigates, remediates and reports.
- Manage riskLower your exposureGaps, compliance and priorities reviewed with you.
↺ and back to monitoring, continuously
See the platform on your own environment
A 30-minute demo, with your questions answered by a ThiRU engineer.